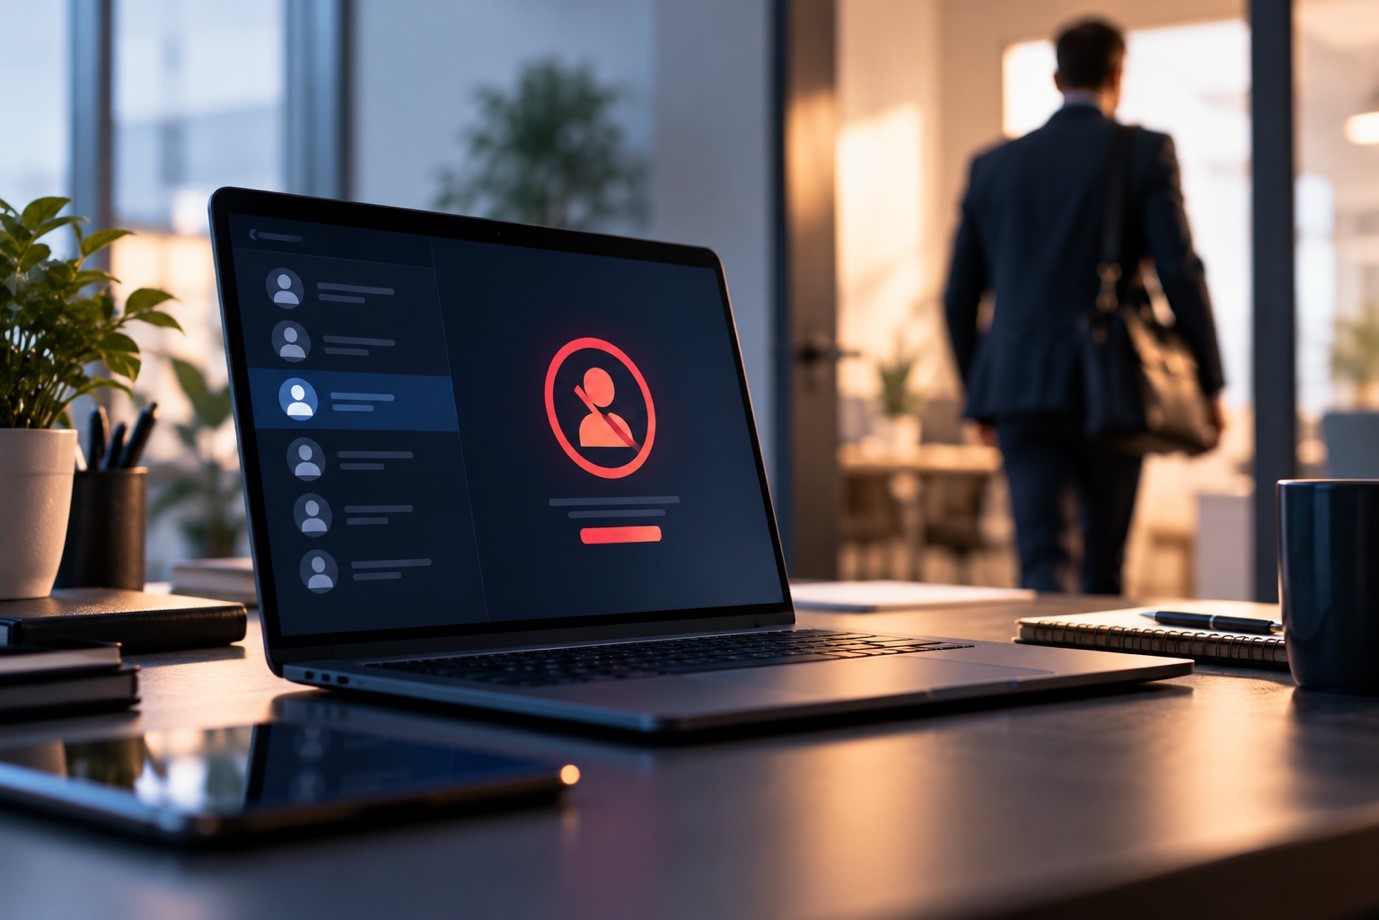
The Overlooked Cybersecurity Risks of Employee Offboarding
The laptop is returned, the farewell email goes out and payroll closes the employee’s file. Then, three weeks later, somebody discovers the former employee can still open the company’s project board.
It is rarely the dramatic breach that exposes a weak offboarding process. More often, it is a forgotten account, a shared password or a client folder nobody thought to check. For CEOs, that makes employee departures a business risk as much as an administrative task.
The Accounts Nobody Remembers
Most organisations have a formal process for collecting badges and devices. Digital access is harder to see. An employee might have permissions across email, cloud storage, finance software, messaging channels and a handful of specialist services purchased by their team.
The problem grows when departments sign up for tools without involving IT. A marketing manager may own the social accounts; a salesperson may have created a customer database; a contractor may still be able to access both.
AI tools deserve a place on that inventory too. If staff use a business AI assistant to review proposals, summarise client material or draft internal reports, leaders need to know who controls access and how confidential conversations are handled. Choosing a service built for business privacy is useful, but it does not replace the need to remove accounts when someone leaves.
A Password Reset Is Not an Offboarding Plan
Disabling the company email address is a start, not the finish. Some services use independent logins. Others allow external file sharing, personal-device access or active sessions that survive a password change until administrators revoke them.
Shared credentials create a further problem: removing one person may mean changing the password for everyone. This is one reason individual accounts, role-based permissions and multifactor authentication are worth the setup effort.
Who receives the departing employee’s customer enquiries? Who becomes responsible for scheduled campaigns, shared documents or automated workflows? Access needs to be removed without accidentally cutting off work the business still depends on.
The Cost Can Extend Beyond a Data Breach
A former employee does not have to act maliciously for damage to occur. Files can be deleted by mistake. Sensitive documents can remain synced to an old device. A paid software licence can continue renewing for months without anyone noticing.
A Forbes article on offboarding risks identifies data loss, confidentiality breaches, compliance problems and unnecessary software costs among the consequences of a poorly managed departure. All point to the same issue: the company has lost track of who can reach its information.
Make Departures a Shared Responsibility
HR knows when someone is leaving. IT knows which accounts exist. Department heads know which projects, clients and tools the person actually used. A reliable process needs all three.
For routine departures, prepare an access checklist before the final working day. For higher-risk situations, coordinate account suspension with the agreed departure time. Recover company equipment, transfer ownership of important files and check external sharing permissions. Keep an auditable record of what was closed and when.
CEO Monthly has also covered the importance of strong access controls in its guide to executive cybersecurity essentials. The principle applies just as much to employees leaving the business as to those joining it: permissions should reflect a person’s current role, not their history with the company.
Review the Process After Every Awkward Case
A forgotten login is useful evidence of a process gap, even if nothing bad happened. Find out why it was missed. Was the software absent from the register? Did the manager assume IT would handle it? Did the account belong to a shared team rather than an individual?
Those answers are more valuable than adding another vague instruction to an employee handbook.
Offboarding is one of those operational details that looks small until it fails. CEOs do not need to personally close every account. They do need to make sure someone is accountable for the full list, including the tools that arrived quietly
Stay updated with our latest publications.
Discover Issues
See how we can help you grow in the online space!
Advertise With Us
We can help promote your business.
Find Out More